Not even the tobacco companies said “this will kill you.”
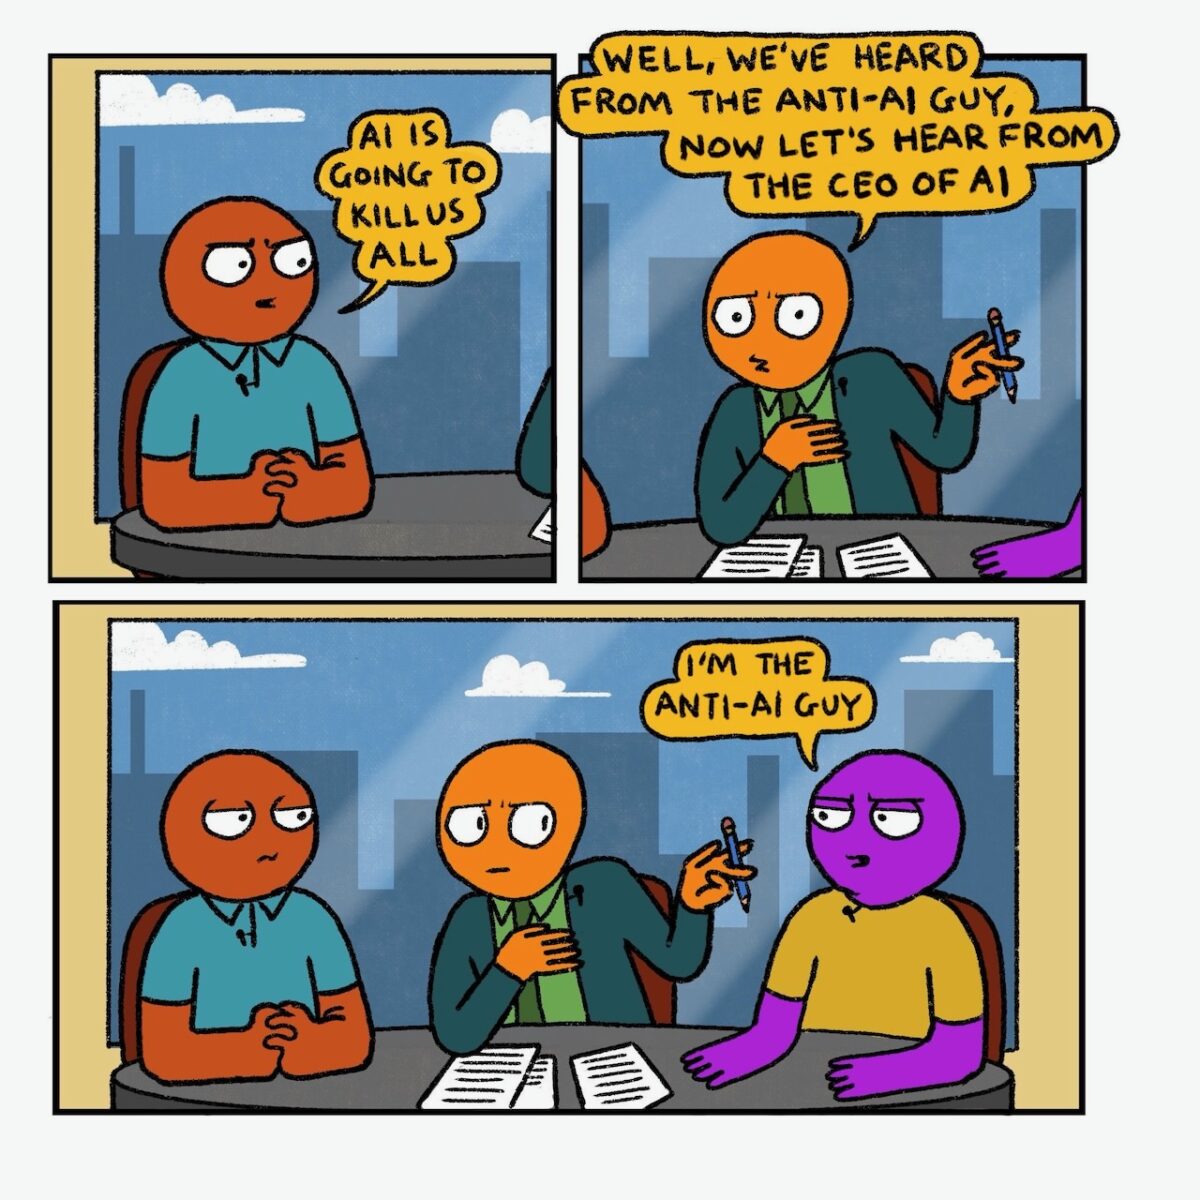
Not even the tobacco companies said “this will kill you.”
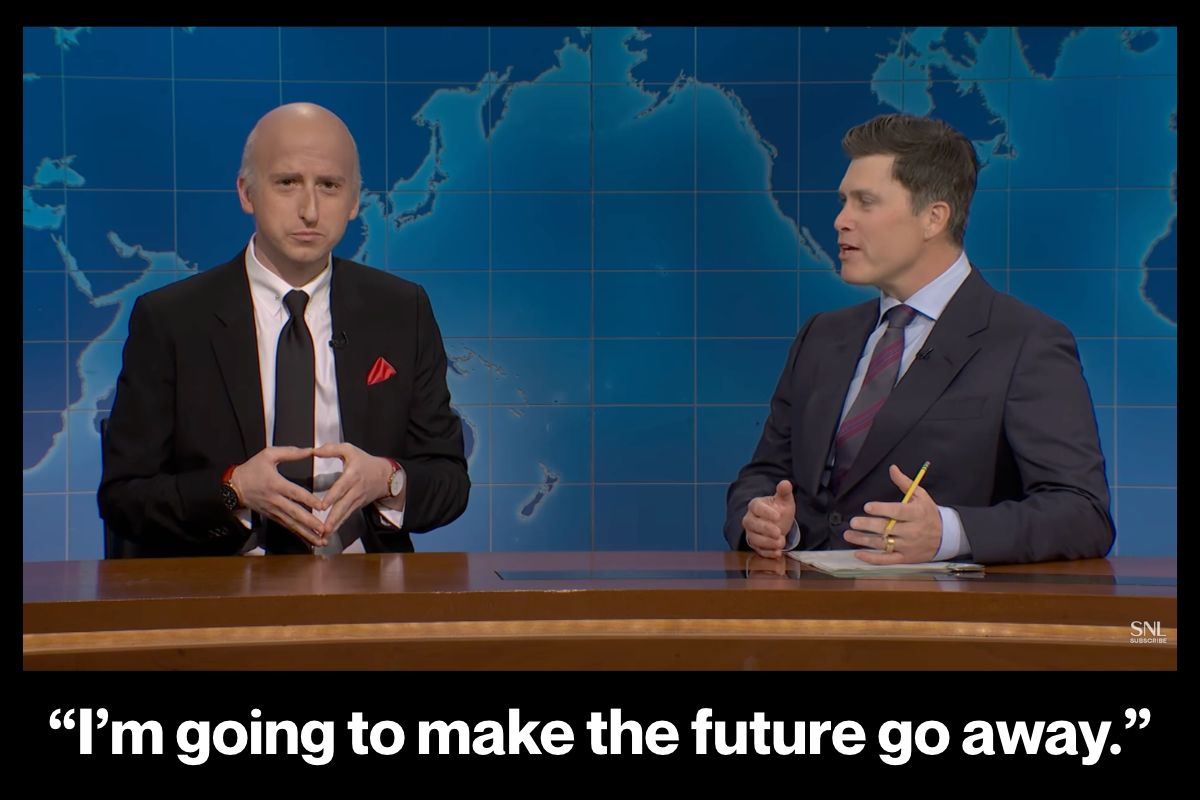
On this Saturday’s Saturday Night Live, the most relevant bit was on the Weekend Update segment where Colin Jost interviewed “Kevin O’Leary” (played by James Austin Johnson) about his plans to build his Stratos data center in Utah and the resistance to his plans.
Here’s the video…
…and here’s the transcript of the skit:
Colin Jost: According to a new poll, 75% of Americans would oppose an AI data center being built near them, making it one of the country’s most unifying issues.
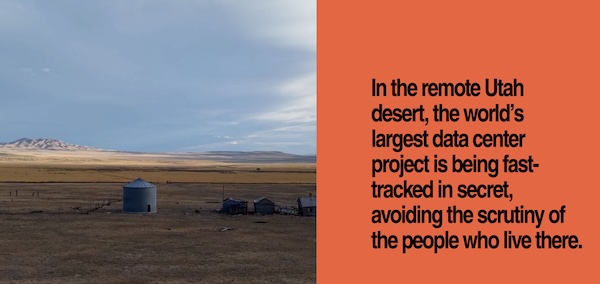
Here to comment is the man who proposed building the world’s largest data center in Utah. “Shark Tank’s” Mr. Wonderful, Kevin O’Leary.
[ Cheers and applause ]
Kevin O’Leary: Thank you, Colin. It’s a pleasure. Thanks for having me.
Colin: Thank you for being here. So what happened, Mr. Wonderful? Protesters in Utah are forcing you to downsize your project?
O’Leary: I’m glad you asked, Colin. And it’s very simple.
All I want is to buy up 40,000 acres of God’s untouched splendor and replace it with a very loud computer that steals your job.
[ Laughter ]
Is it going to take up precious water? Absolutely.
Is it going to provide a necessary service? Who’s to say?
But on the flip side, it’s going to make me a tremendous amount of money. And I think that’s great.
[ Laughter ]
Colin: Right.
Well, most Americans don’t want data centers near them.
O’Leary: And I agree with them completely.
Colin: You do?
O’Leary: Of course, Colin.
These things are terrible and shouldn’t be anywhere. That’s why I’m building one in Utah.
And this is actually very simple. I’m going to show you on this map.
Alright? See, this is Stratos, my data center with the most evil name of all time. And sure, it looks big.
The noise and water pollution? That’s only going to affect this area. Colin, you have to understand, I don’t live there.
[ Laughter ]
Colin: Right. But, like, other people do live there.
O’Leary: You’re missing the point. That’s not real to me. Okay?
Those people’s lives, those are Sims. Alright?
Look, I’m a numbers guy, okay? When I missed out on investing in Scrub Daddy, I learned a very valuable lesson, which is I’m going to destroy the world.
[ Laughter ]
Colin: That sounds pretty extreme.
O’Leary: Well, that’s because you’re poor.
[ Laughter ]
Colin: Actually I’m not. My wife gives me lots of spending money.
[ Laughter ]
[ Cheers and applause ]
Colin: [to the camera] That’s not nice.
[To O’Leary] And aren’t you being sued for defamation in Utah?
O’Leary: Look, yes, I made the mildly inflammatory claim that every single person in Utah who opposes me is a paid communist super agent from China.
Was I wrong? Perhaps. But just because they’re not, doesn’t mean they aren’t.
Colin: What?
O’Leary: Look, Colin, when I missed out on Bombas socks, I could have gotten mad. But instead I made a decision.
I’m going to make the future go away. And we’re doing just that in Utah.
Colin: Mr. Wonderful, everyone.
[ Cheers and applause ]
O’Leary: And for that reason, I’m out.
Ain’t livestreaming grand? We had a few rough-around-the-edges moments in today’s episode of Ziti TV (I worked on the demo a *little* too late last night), but the important thing is: THE DEMO WORKED.
The demo built on the previous episode’s work where we took the OpenZiti Appetizer (a service that displayed whatever text you feed it on a public web page via a secure zero-trust OpenZiti overlay) and added a RoBERTa classifier to it to prevent users from entering offensive messages for the Appetizer to display. There are lots of people out there who seem to not have aged past 12, and that’s what this is supposed to handle.
RoBERTa classifiers are good at handling profanity and direct insults like “You are too stupid to understand this”. It *will* miss more subtle jabs like “Nobody wants you here and everyone knows it”, but try saying that to a cop who’s writing you a speeding ticket, and they will classify it very differently.
So in this week’s, the classifier keeps its job, but when it isn’t sure, it asks for a second opinion. LLM Gateway, the OpenZiti-based open source OpenAI-compatible gateway, decides which LLM gives that opinion: a small model on your own machine for everyday messages, and Claude for the subtle ones. You won’t change a line of the Appetizer’s code.
I did the demo without much chance for a rehearsal, and I’ll post a GitHUb repo with all the steps and material you need to try it out for yourself. But in the meantime, catch Clint and I work our way through the demo!
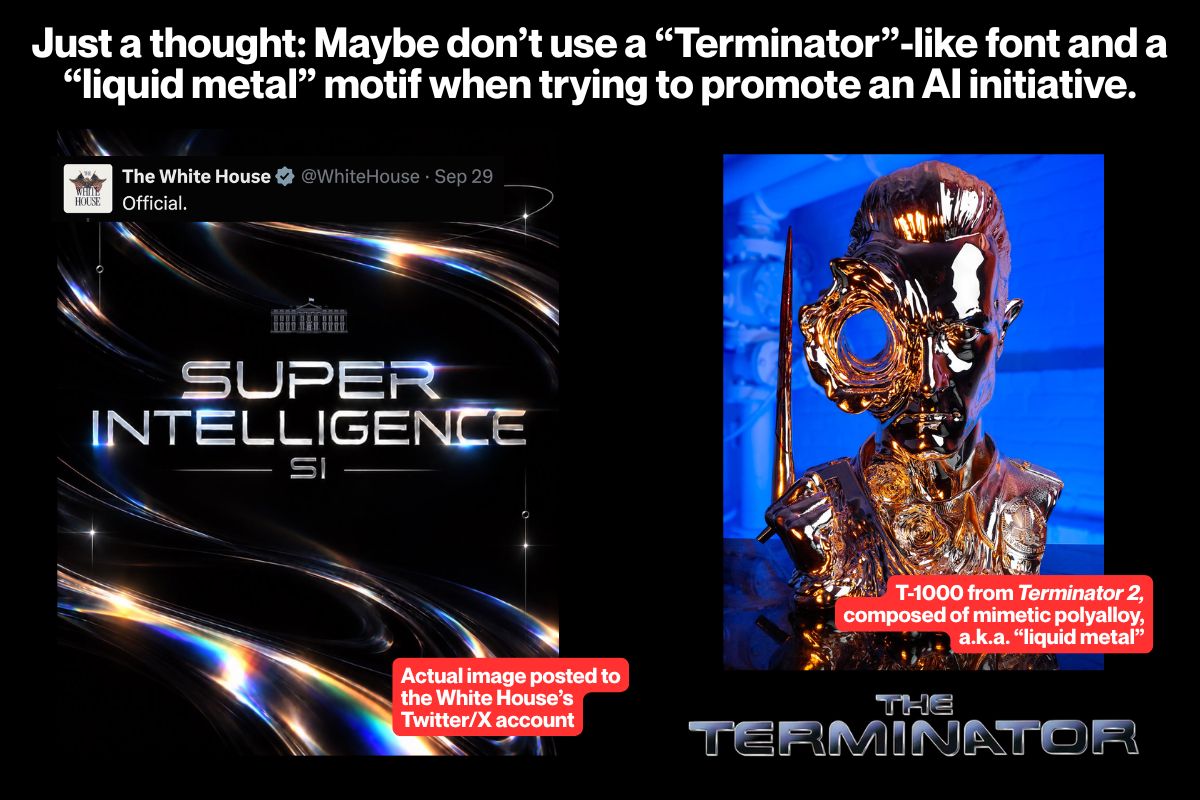
Yup, that’s an actual Tweet from the official White House account. That’s another data point for the “Everyone is 12 now” theory.
I’m just sayin’: if you’re trying to promote AI as a beneficial thing, maybe the whole Terminator 2 motif is something you might want to avoid. Those AIs, Arnie’s T-800 excluded, were not our friends!
In the meantime, let’s enjoy the classic line from that film:
If there’s one thing that Donald Trump and his sycophants love to do, it’s name or rebrand things to name them after hinself, make them sound more “extra”, or both. Consider:
…and the list goes on.
And now the idiocy meaningless renaming has come to tech:
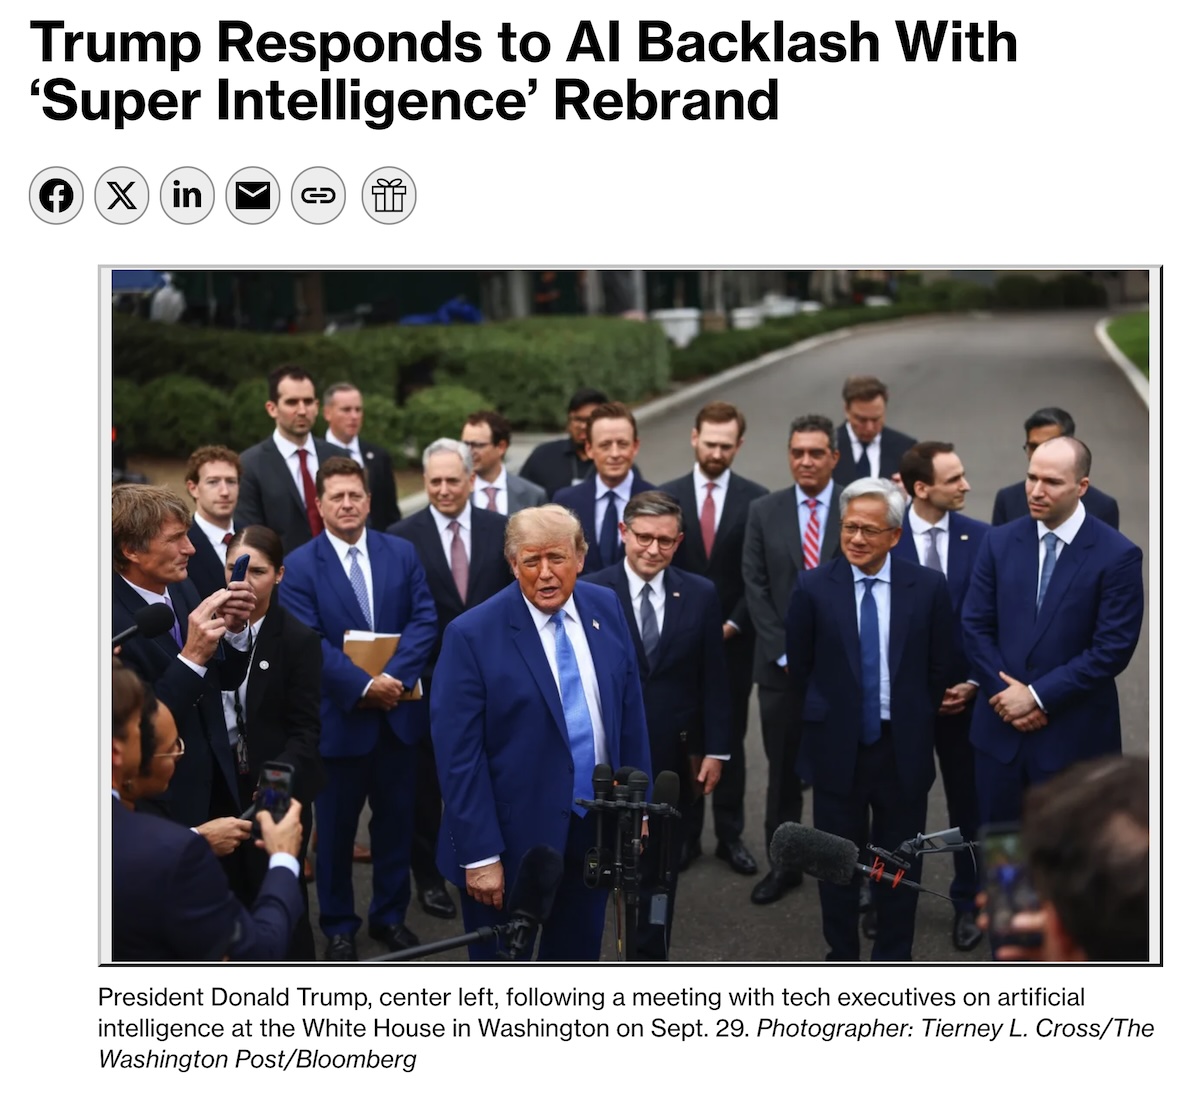

The executive order, titled INAUGURATING THE ERA OF SUPER INTELLIGENCE, basically declares that “AI”, a term that we’ve been using since 1955 when John McCarthy coined it, should now be referred to as “Super Intelligence” or “SI” in executive-branch communications.
It says that agencies of the federal executive branch must use the new terms in official correspondence, public communications, websites, reports, policy documents and other non-statutory documents. Thankfully (because it would mean a lot of pointless work otherwise), existing regulations, presidential actions, contracts, grants and historical documents don’t have to be changed.
It also means that any content I make aimed at a U.S. government buyers or techies (especially tutorials, presentations, and documentation) will need to include the “SI” terms for both practical (for example, search terms) and political (“We call it ‘SI’ here, son.”). I’m already not looking forward to this.
For now, “SI” means exactly what “artificial intelligence” already means under 15 U.S.C. § 9401(3).; only the name has changed.
Sometime in the next 60 days, Michael Kratsios, the Director of the White House Office of Science and Technology Policy (OSTP), will have to propose legislative language for a federal definition of SI. It’ll have to say whether that definition should modify or replace the statutory definition of AI, and include any conforming amendments and follow-on executive actions. If such changes are made, expect them to be dumb.
Unsurprisingly, it didn’t take long for the first kiss-ass to use the term in Trump’s presence:
https://www.youtube.com/watch?v=GzKZwuUJWJQ
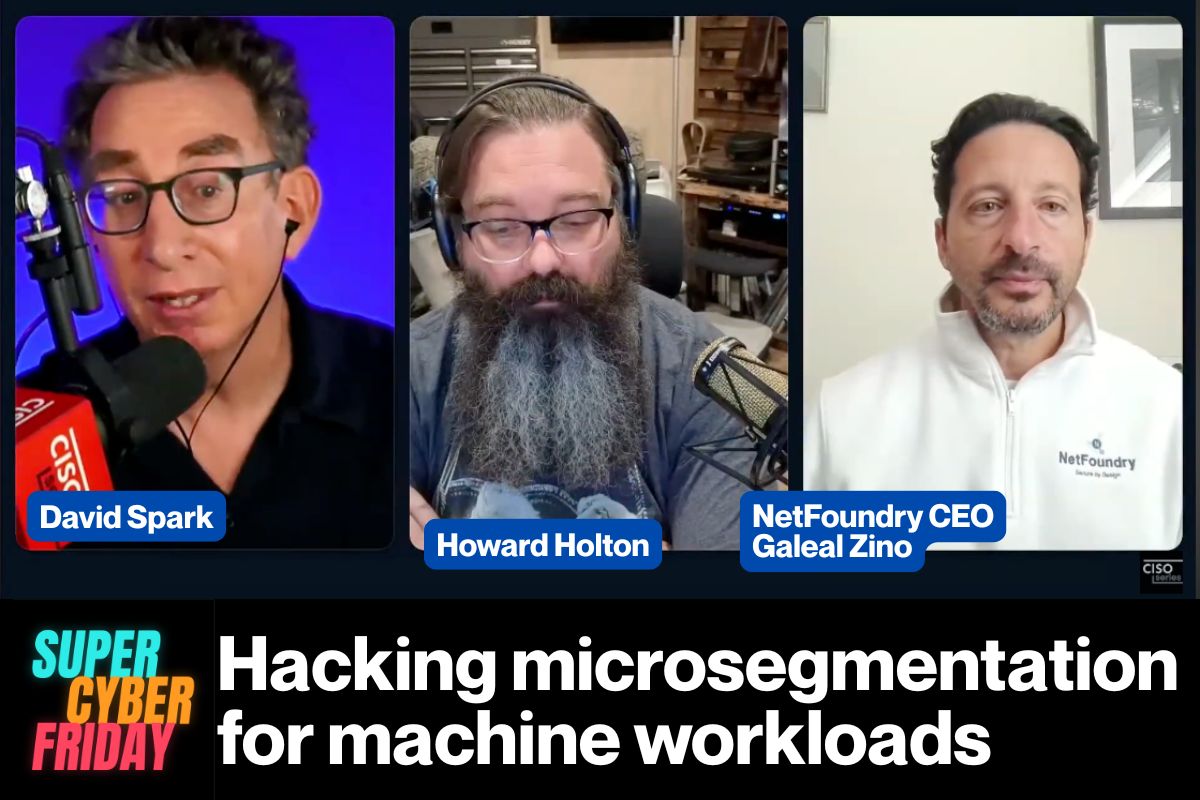
 Last Friday, NetFoundry’s CEO Galeal Zino appeared on the weekly live YouTube show Super Cyber Friday, hosted by tech journalist David Spark.
Super Cyber Friday is about cybersecurity practitioners and vendors, and every episode has a title that follows a “Hacking [Topic]” format. This particular episode’s title is Hacking Microsegmentation for Machine Workloads, and features:
If you’re wondering what microsegmentation is, here’s the short version:
Microsegmentation is the practice of carving your network into tiny zones so that when something gets compromised (and something will), the damage stays in one small room instead of spreading through the whole house.
Everyone agrees it’s a good idea, almost nobody enjoys doing it, and few actually do it. It’s the brushing and flossing of cybersecurity.
You should know:
Feel free to apply the appropriate amount of skepticism to this writeup, but keep in mind that this episode features both a CEO who builds security stuff with an analyst who’s had to live with the results. The episode’s a little more blunt than your typical PR piece.
C’mon, this article isn’t that long! But still, if you want a very quick summary, here it is…
| The old way | What machine workloads need | |
| What you segment by | IP addresses, subnets, CIDR blocks, VLANs | A cryptographic identity for every machine, plus attestation |
| Where enforcement happens | Firewalls and middleboxes at the edge | Inside the application, via an identity-driven overlay |
| How AI agents get treated | “It’s basically an employee” or “It’s basically an app” | As a non-human actor with explicitly bounded access |
| What failure looks like | Firewall surgery, configuration bloat, shelfware | A contained blast radius |
| What the board says | “We better never get hacked.” | “How bad will it be when we get hacked?” |
Howard set the tone in the first minute, when David asked for his microsegmentation pet peeve (0:08):
“Early microsegmentation sucked so bad that it’s hard to get people to listen when you talk about microsegmentation.”
For the record, Howard is a big microsegmentation fan. What drives him (and us at NetFoundry too) up the wall is the feedback he hears most often: “Nope, we did that before, we’re not doing it again.” People tell him it was too complicated and a waste of money. He hates that feedback because, in his words, “it’s just wrong.”
Later in the show (7:25), he explained how early rollouts earned that reputation. Teams would get frustrated during the discovery stage, put some segments in place, and then cause an outage by blocking something that only ran once every 30 days and that nobody had planned for. After that happened a few times, they’d shelf whatever microsegmentation tool they were using. His summary: “Complexity always bites you in the ass.”
If you’ve ever been anywhere near a rollout like that, you probably just winced. The problem wasn’t the idea. Least privilege and blast-radius reduction are good ideas! The problem was that vendors tried to implement them with the tools that just happened to be conveniently lying around: IP addresses, subnets, VLANs, and firewalls.
When an audience member asked whether application-level or network-level microsegmentation is more effective, Galeal didn’t mince words (9:05):
“Network-level is DOA: dead on arrival. It’s an oxymoron to begin with… It’s spilled milk, and you can’t put it back in the bottle. If you’re going to try and use IP addresses, VLANs, and firewalls to do ‘microseg,’ good luck to you. It’s not going to happen.”
That’s coming from someone who’s been doing network engineering for 30 years. Here’s the core problem, especially for machines: an IP address tells you where something is, not what it is. In a world of containers, autoscaling, and serverless functions, the IP address your billing service has this morning might belong to something completely different by the time lunch rolls around. Writing security policy against IP addresses is like keeping track of your friends by remembering which seats they sat in the last time you all went to the movies. Or, as Galeal put it later in the show (35:10), “IP addresses are not identities.”
Howard then described what happens when you try to brute-force it anyway (10:03):
“Microsegmentation and segmentation are not the same thing… If you’re like, ‘Well, I’m going to create 437 subnets in my network and I’m going to create 300 VLANs and I’m going to turn on host-based firewalls,’ you’ve just created a nightmare that no one is ever going to be able to manage after you. And you have failed job number one, which is make sure that the next person can be as successful as you are.”
“Make sure that the next person can be as successful as you are.” I want that on a poster, and not just for network engineers. It applies to code, documentation, and pretty much anything you build that someone else will inherit.
And if you try to do it the classic way regardless, making your firewalls enforce all that traffic between your services? According to Galeal (29:48), that’s the first lesson you’ll learn: “You will melt your firewalls.”
My favorite moment in the episode came from an audience question. Sierra Montgomery asked (11:05):
“If a compromised workload acquires valid credentials and begins behaving like a legitimate service, what signal does your microsegmentation architecture use to distinguish legitimate machine-to-machine communication from lateral movement?”
Galeal’s answer was one word: Attestation. His reasoning: a credential doesn’t prove whether Howard, David, or an AI agent should have it. Credentials, he said, are “necessary but not sufficient.”
Explaining bearer tokens is something that goes back to my first article for Auth0, which was also my “take-home assignment” in the job interview process. The concept always needed the most careful explaining, even though the name told you everything: whoever bears the token gets the access. The token doesn’t know or care who’s holding it. It’s more like cash than a credit card.
That’s fine as long as you know where the token is. The trouble starts when you don’t. A credential proves that something possesses a secret. It doesn’t prove that the thing should have that secret, and it says nothing about whether the machine presenting it is in the state it’s supposed to be in. Attestation fills that gap: it’s verifiable evidence that the workload is what it claims to be, and that it’s running where and how it’s supposed to.
At a DEF CON party a long time ago, a few friends and I came up with a joke talk title for the following year’s edition of the conference: “Security is for lightweights. Take the pwning like a champ.”
 But behind the joke was an important idea: every boxer gets hit. What makes a champ isn’t never getting punched; it’s being able to take the punch and stay on your feet. Security works the same way. Sooner or later, one of your credentials is going to end up in the wrong hands, whether it’s through a phished password, a leaked API key, or a token that got copied out of a log file. Back then, planning on getting pwned was a punchline. These days, it’s a design principle, and it’s exactly where Galeal starts.
The DEF CON joke came to my mind when an audience member asked how a platform can alert on a compromised token moving laterally (16:06). Galeal’s answer was in the spirit of “Take the pwning like a champ”: Assume that tokens will be compromised, and design your system so that a token by itself doesn’t grant access.
If your architecture opens the door and grants network reachability before it verifies identity, an ill-gotten token can be a starting point to explore your network. The “Take the pwning like a champ” approach that NetFoundry takes verifies identity first and uses policies to spells out which identities can talk to which services. A stolen token doesn’t open any new doors, because the path the attacker wants isn’t accessible to them.
 History time! If you were a developer around the time the iPad came out, you might remember Chaos Monkey, Netflix’s tool designed to randomly shut down servers in production. The idea behind it could be summarized as “The random shutdowns will continue until resiliency improves”. Netflix’s dev teams were forced to build in such a way that their systems would survive failure. It’s a brilliant (if sadistic) idea, and it works because Netflix chose to unleash it deliberately, with rules.
This isn’t all too different from a pattern Galeal described (28:56): taking an AI agent and saying, “Hey, cool. Here’s some API keys. Here’s the internet. Here’s some enterprise resources. Go do something useful.”
Howard’s response: “I see that like 40 times a week.” That’s a chaos monkey too, except nobody scheduled it, nobody wrote the rules, and it will explain its reasoning very confidently afterward.
My last job prior to my current Developer Advocate gig at NetFoundry was optimizing an MCP server, so this isn’t a hand-wavey “some customer has this issue” thing to me. Every tool or function you expose through an MCP server is something an agent can decide to call, whenever it wants, for reasons you didn’t anticipate. Its network traffic doesn’t follow a script.
When an audience member asked how to segment an AI agent whose needed connections change with each task, Howard’s advice was (27:27):
“If you try to design something that is entirely flexible, what you’re going to end up with is opening yourself up for AI chaos in your network… If you do it the other way around and hope that your microsegmentation tool set is going to keep up with your AI, you’re basically saying, ‘I want microseg to follow my chaos monkey.’ Do it the other way around. Use microsegmentation to restrict the chaos monkey.”
Galeal’s answer to the same question (26:43) supplies the other half: The old bag of tricks isn’t going to work on agentic flows. Treat agents as identities, define a graph of what each one can talk to and under what conditions, and have the visibility and enforcement to make sure they stay on that graph.
That’s the right mental model. An AI agent isn’t a human employee sitting behind your SSO portal, and it isn’t a cron job that does the same thing at the same time every night. It’s a whole new thing.
As Howard put it later in the show, it isn’t another application, and it doesn’t act like a human either. It needs boundaries defined up front, including things like:
Time for me to put my work hat on for a minute. The table above mentions “an identity-driven overlay” enforced “inside the application,” which is a mouthful, so here’s what it means in practice.
OpenZiti is the open source zero trust networking platform that NetFoundry builds, and one of the things it lets you do is embed zero trust directly into your application with an SDK. Your app gets its own cryptographic identity, and it can only reach the services that policy says it’s allowed to reach. On the other side, services don’t need open inbound ports at all, so there’s nothing sitting on the network for an attacker to scan, probe, or point a stolen token at.
Galeal’s “kill switch” (more on that below) gets pretty concrete here too: if an identity is compromised, you revoke it or change the policy, and its paths go away. No firewall surgery required.
 If you want to try it yourself, the docs and quickstarts are at openziti.io.
Near the end, David read an audience question: Which metric best shows leadership that microsegmentation is working? Galeal boiled his answer down to three questions (39:11):
Then Howard put on his gloves (41:27): “I couldn’t disagree more.” Speaking as a CISO, he said:
“What my board said 10, 15 years ago was, ‘We better never get hacked.’… Today they say, ‘How bad will it be?’ That is their question to me. That is the question they want me to answer in every board meeting they invite me to.”
My answer would be “Take the pwning like a champ”.
David pointed out that the two answers aren’t really in conflict: Galeal was describing what you measure for yourself and your security team, and Howard was describing what you tell the board. Galeal agreed. Howard then explained why the board version has to be so compressed (43:29):
“I get one slide as a CISO… I get like five minutes… I make that one slide tell them how I’m spending money to make it less bad than the last time they gave me money.”
Ah, the dreaded “You get one, and only one, slide” directive for board meeting presentations. Replace “board” with “VP of Engineering” or “whoever approves your budget,” and it’s still excellent advice.
If I had to boil the whole episode down to one idea, it wouldn’t be about AI, firewalls, or attestation. It would be Howard’s “job number one”: make sure the next person can be as successful as you are.
Galeal landed in the same place from a different direction. When David asked why he started NetFoundry (24:00), he said that after years of beating his head against walls like microsegmentation, he wanted to tilt the playing field so that the next person who has to solve these problems doesn’t have to.
That’s the real case against building microsegmentation out of subnets and VLANs. Even if you get it working, you’ve built something nobody else can understand, let alone maintain.
A policy that says “the billing service can talk to the orders database, and the AI agent can talk to these three APIs and nothing else” is something the next person can read, reason about, and change without breaking everything. And when some of the things doing the talking are AI agents that nobody can fully predict, that kind of clarity is what keeps the chaos monkey in its cage.
Go watch the episode, and if you’re a developer who wants to see what identity-first networking looks like from the inside, take OpenZiti for a test drive!
I’m a few days late on this one, but the content holds up: last week’s Reachability Watch, written by our Chief Strategy and Marketing Officer Mark Jaffe, covering September 11–17, is here:
https://netfoundry.io/ai/reachability-watch-cve-kev-tracker-2026-09-18/
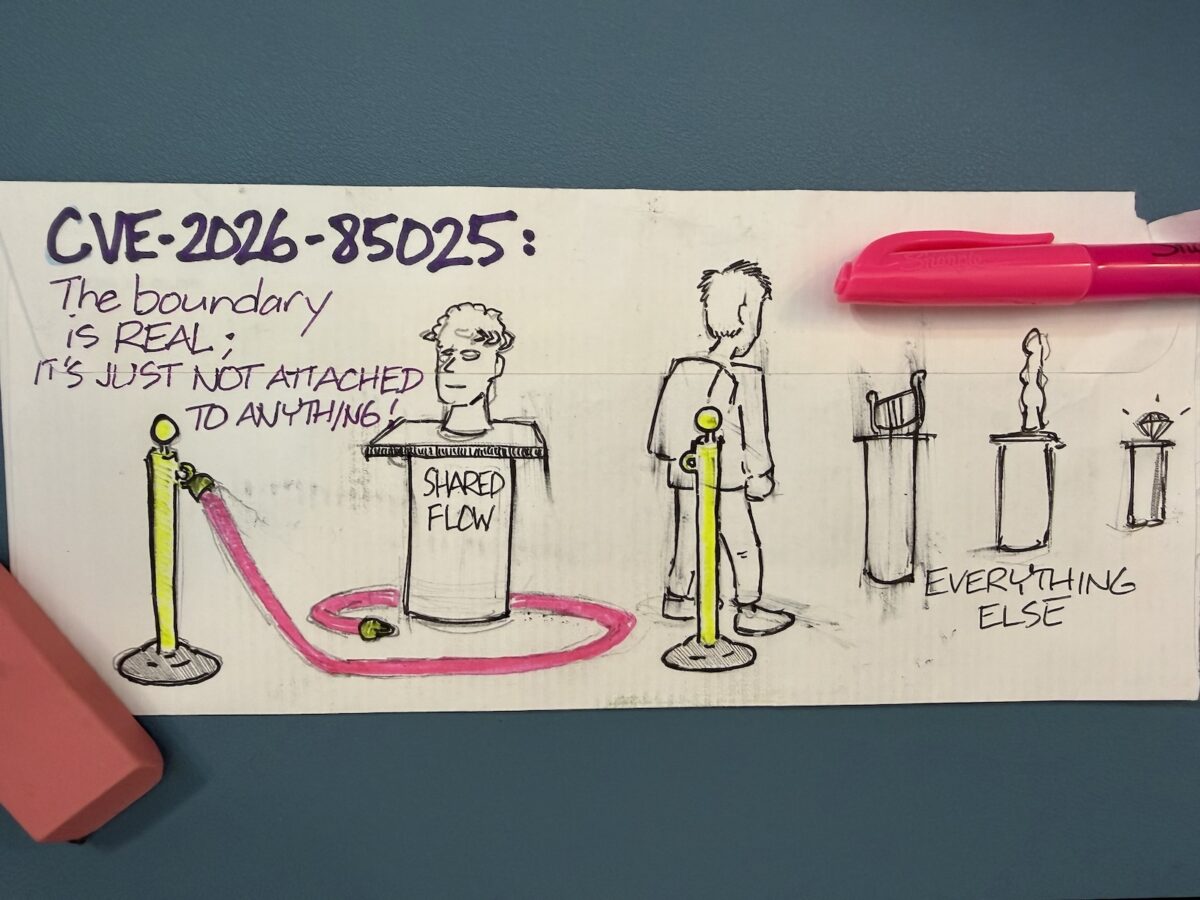
(On the bright side, I had time to draw a “back of the envelope” comic that covers the big CVE!)
Here are the numbers:
CVE-2026-85025 (9.8) is unauthenticated RCE in IBM Langflow OSS 1.0.0–1.11.5. It’s reachable through publicly shared MCP project endpoints, with read and write access to chat sessions on top. Whatever context, credentials, or proprietary data flowed through those sessions comes along with it.
The mechanism is the interesting part. Langflow lets you share a flow via an MCP project endpoint so other tools and agents can call it programmatically. The code that’s supposed to enforce “this one flow is public, everything else isn’t” doesn’t hold that boundary. So “publicly shared” quietly generalizes from one flow to the host. This happens without a privilege escalation chain, user interaction, or even any waiting for someone to click anything.
All in all: 8 CVEs against Langflow in a single seven-day window, including the one above: code injection, OS command injection, path traversal, an incomplete scanner denylist, and this one.
Mark writes that he’d bet money that the Langflow flaw above becomes a KEV. Another Langflow CVE has already done that: CVE-2025-3248, a missing-authentication RCE, which went onto CISA’s KEV catalog on May 5, 2025, with a three-week federal remediation deadline and confirmed ransomware use. Sysdig later documented that same flaw on a server nobody had patched in over a year as the entry point for what they assessed as the first fully autonomous agentic ransomware operation.
The traits that move a CVE onto KEV are the traits this one has: no auth, trivially scannable, and sitting on infrastructure that isn’t in anyone’s asset inventory. Langflow has supplied both ends of that pipeline before.
Because these tools are three things all at once:
…and they’re shipped by teams optimizing for getting an AI capability out the door. As a result, exposure and hardening get less scrutiny than they’d get on a mature enterprise system.
The part that makes them worth an attacker’s time specifically: compromising one doesn’t get you a single host, it gets you the whole key ring. The same property that makes the platform useful is what makes the blast radius large, which is why “it’s just an internal tool on a dev box” ages so badly.