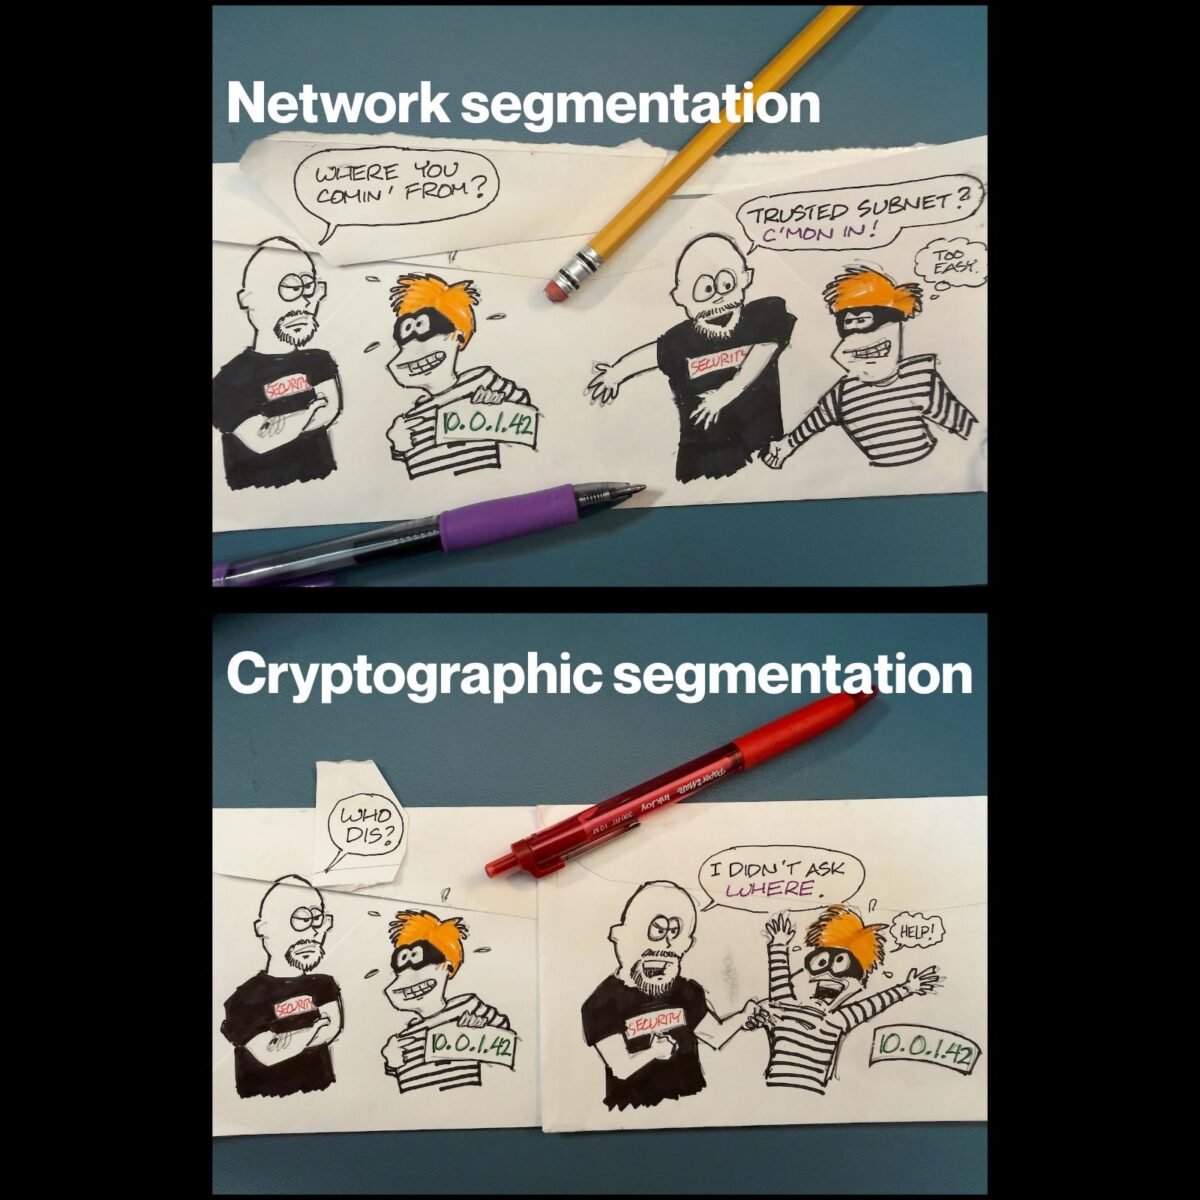
 NetFoundry’s VP Product Marketing Jack Poller has been writing a series of posts on the NetFoundry blog about microsegementation, and I’ve been doing supplementary “back of the envelope” to illustrate what he’s talking about. Jack’s latest piece is on network segmentation vs. cryptographic segmentation, and it made for a perfect four-panel comic, pictured above.
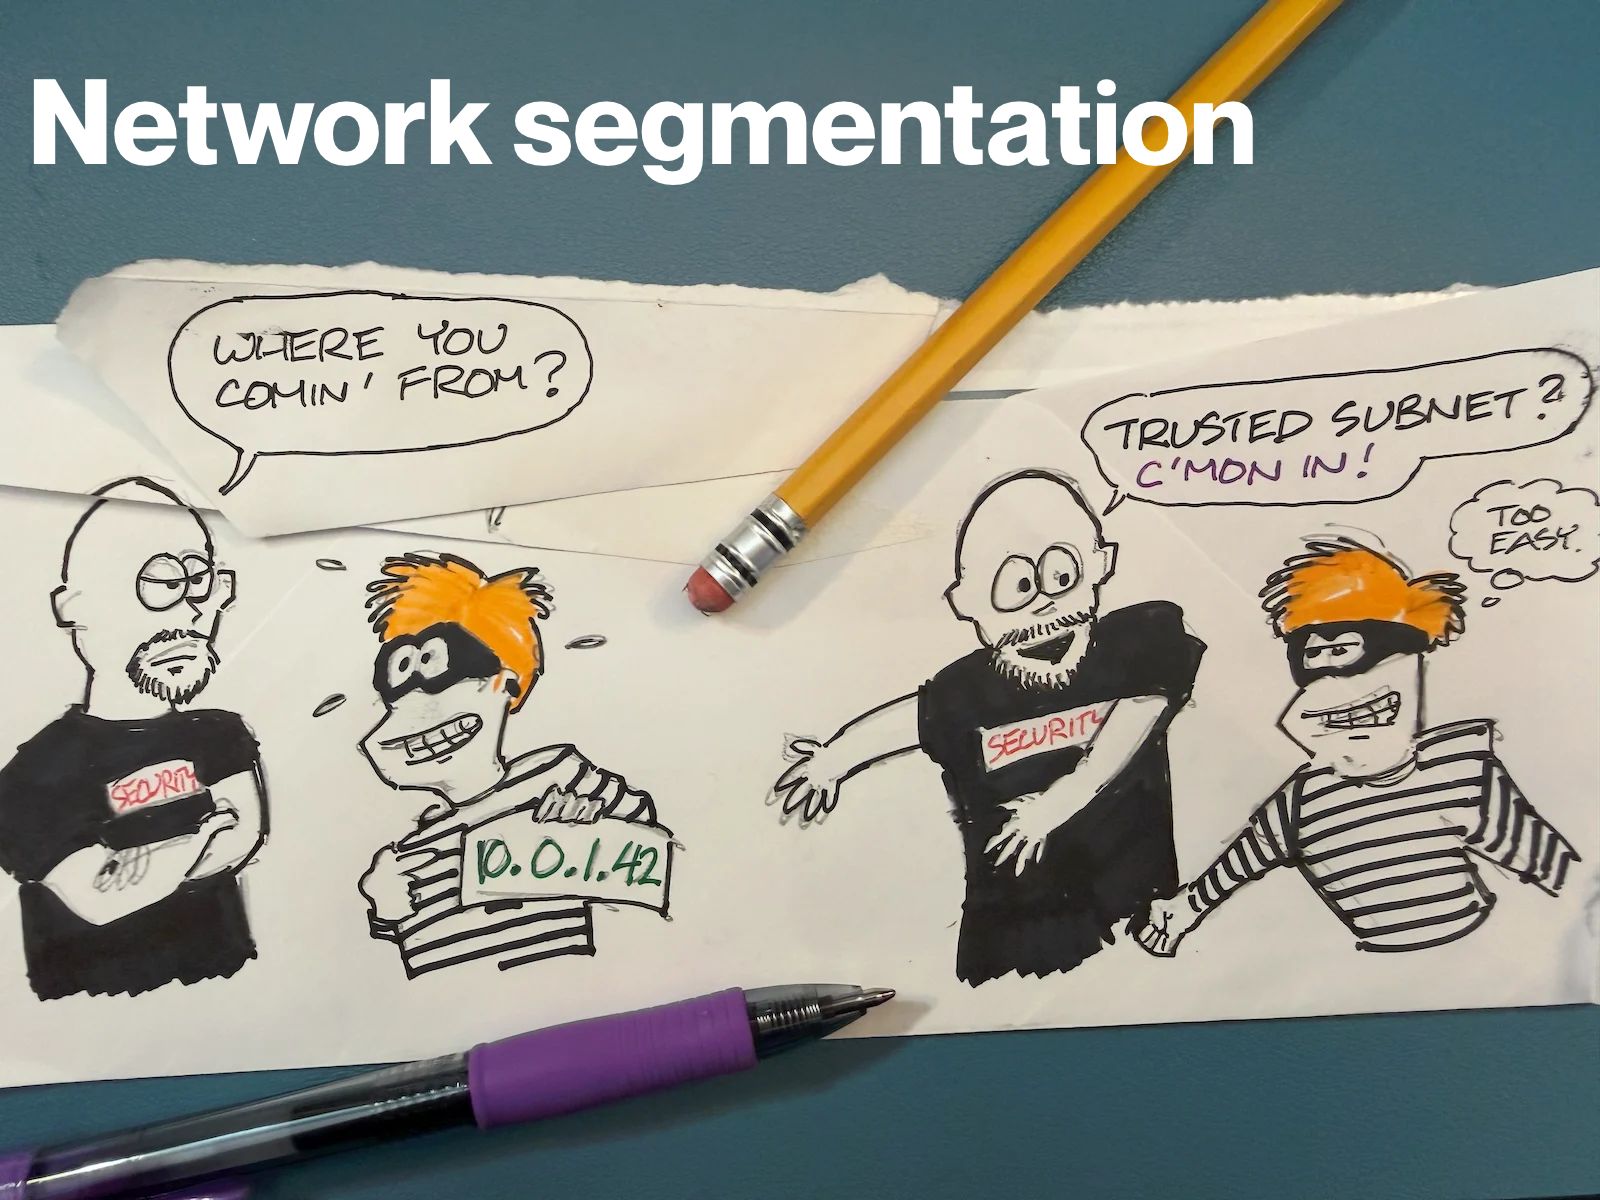
Network segmentation decides trust based on where a connection comes from (that is, its IP address). The problem is that an attacker who’s phished a valid credential or exploited host at a trusted address is already coming from the right place. Host-based firewalls narrow things down to the individual workload, but they run on the same machine that the attacker has “pwned”.
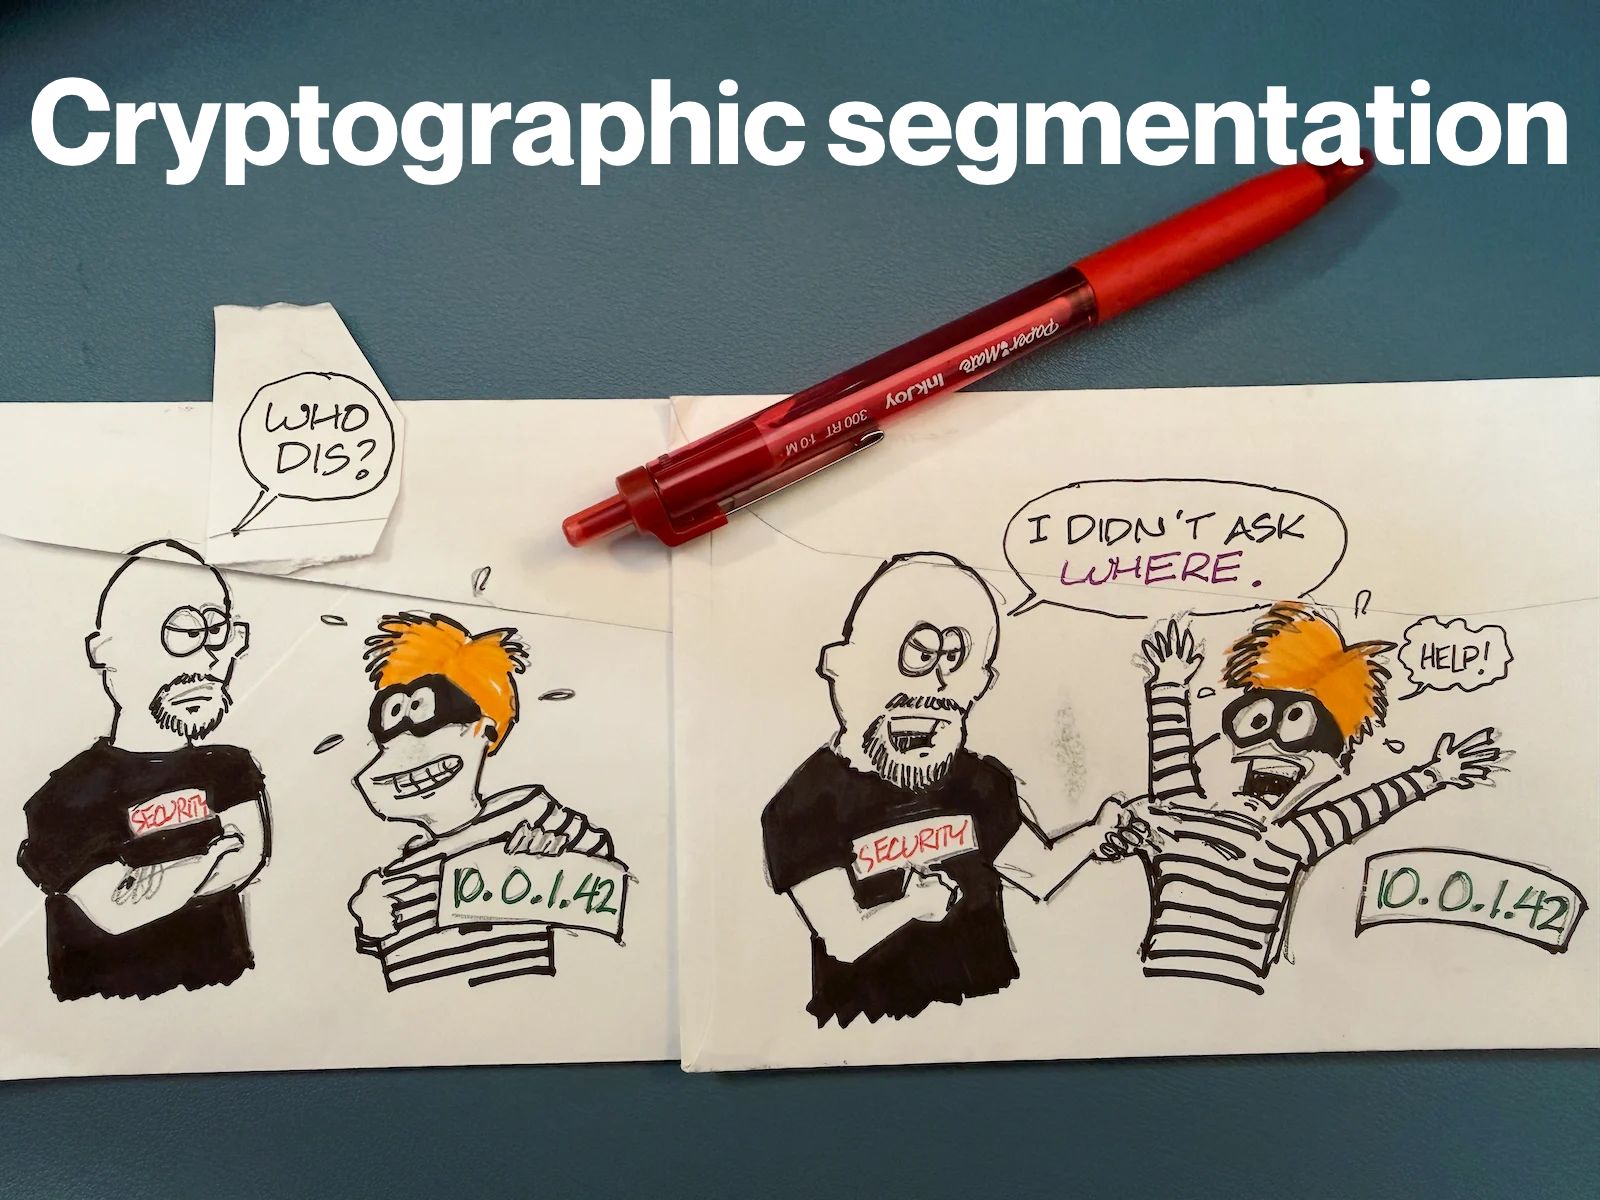
Cryptographic segmentation is another approach, and it’s the alternative that Jack presents. Every endpoint has an X.509 identity, and both ends verify each other with mTLS. A session starts if and only if a policy says that the identity is allowed reach that service. The IP address doesn’t come into play, so coming from “a good neighborhood” doesn’t give the attacker a way in.